Critical Security Vulnerability CVE-2026-18963 affecting UKA Solutions Versions 25.1.0 – 26.1.1
UKA Solutions uses the Keycloak component for authentication. Keycloak versions 26.0.0 through 26.7.1 are affected by the vulnerability «CVE-2026-18963 Unauthenticated account takeover via reset-credentials flow bypass».
This vulnerability allows an attacker to manipulate the password reset process in such a way that they can set a new password for any account whose username or email address is known to them, thereby taking over the account.
The affected UKA versions are 25.1.0, 25.2.0, 25.2.1, 26.1.0 and 26.1.1
As an immediate countermeasure, we recommend disabling the «Forgot password» feature in UKA Solutions. This will ensure that UKA Solutions can continue to operate securely.
Recommended steps to address the vulnerability
Step 1: Log in to UKA Web using a user account with the role «Admin technical IT settings»
Step 2: Open the «Admin Console»
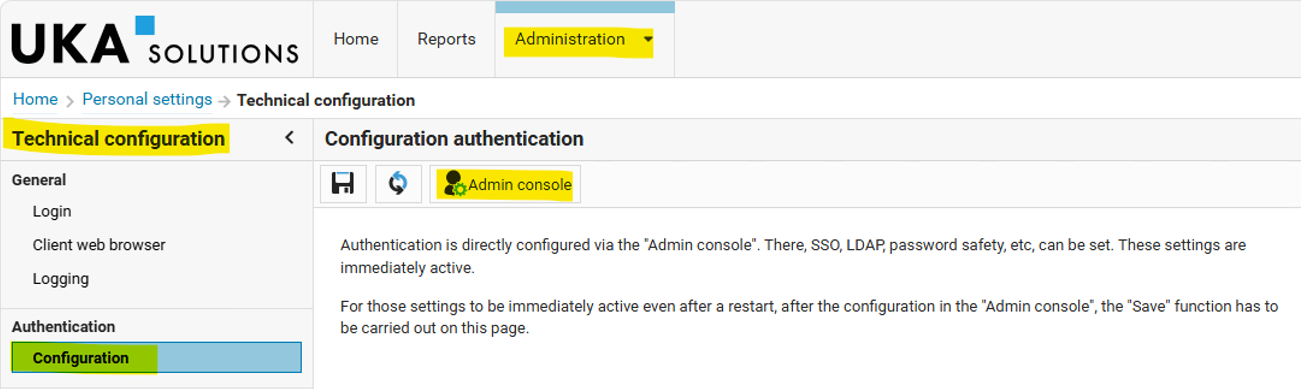
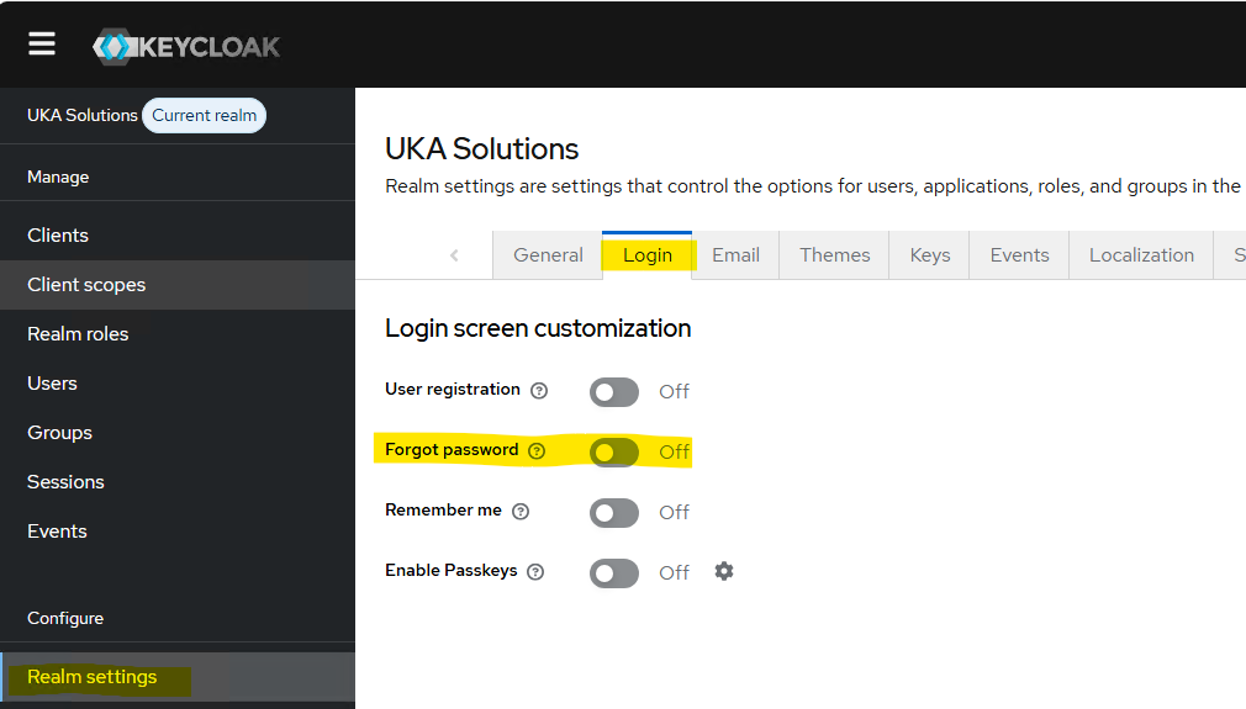
Step 3: Deactivate the «Forgot password» feature
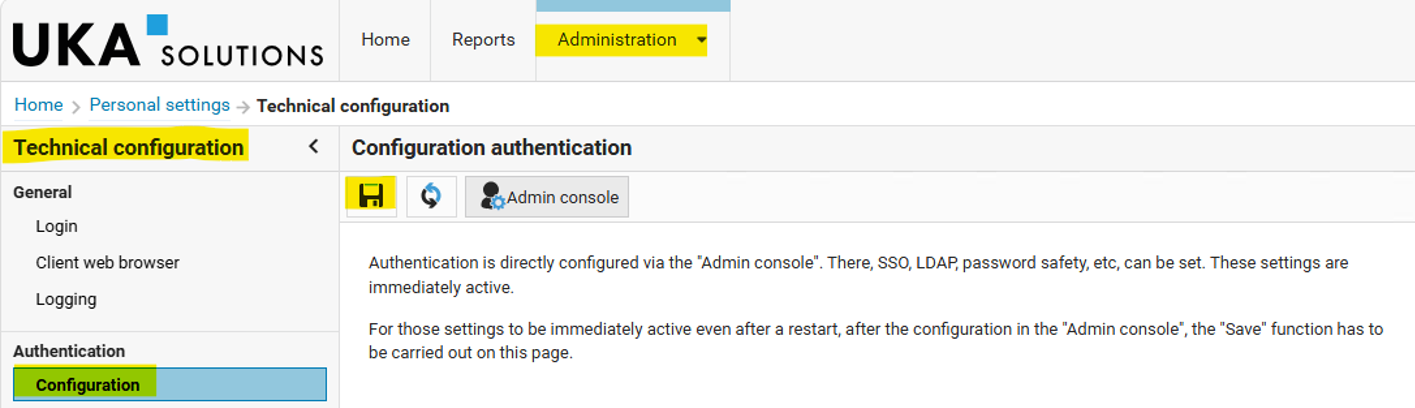
Step 4: Save the authentication server configuration in UKA Web to ensure it remains effective after a service restart
Step 5: A restart of the «UKA Solutions Webapp» service is not necessary. The fix is effective immediately.